Custom Software Development: Engineered for Operational Autonomy
For operations that outgrew spreadsheets and disconnected tools: one web platform with logins, roles, records and reports. We map the workflow first, then build module by module so the business keeps running throughout.
Best for growing businesses in India, the USA, UK, Australia and Canada where you run repeatable operations — bookings, jobs, inventory, billing — across sheets, email and people, and need one system with roles and an audit trail. Staged fixed-price phases; stop after any working release.
Executive Brief
Strategic Context & Engineering Purpose
How our custom software engagements de-risk operational transitions and produce enduring software assets.
Operational Challenge
Mid-market enterprises and high-growth operating businesses frequently reach an operational ceiling where off-the-shelf software and spreadsheet patchworks actively constrain commercial growth. Core operational processes—such as custom quoting, multi-stage job dispatching, distributed inventory allocation, milestone billing, and regulatory compliance reporting—become fractured across five to ten disjointed SaaS subscriptions and fragile manual spreadsheets. This operational fragmentation causes severe data reconciliation drift, employee burnout from duplicate administrative data entry, elevated human error rates, and security vulnerabilities stemming from uncontrolled credential sharing. Furthermore, commercial off-the-shelf software imposes rigid architectural assumptions that force companies to alter their competitive operational workflows to match vendor limitations, all while extracting compounding monthly per-seat licensing taxes that fail to generate enduring enterprise intellectual property.
Architectural Approach
We design and build bespoke enterprise software platforms that model your exact competitive operational workflows as a single, unified system of record. Starting with a rigorous technical discovery and domain modeling phase, our senior systems architects map end-to-end information flows, operational invariants, and role boundaries before authoring code. We engineer modular monoliths or event-driven microservices using strict TypeScript, PostgreSQL, and enterprise cloud infrastructure that consolidate fragmented operational tools into one cohesive web platform. Every data mutation is enforced through transactional ACID database boundaries, deterministic state machines, and fine-grained role-based access control (RBAC). Our development pods operate directly inside your GitHub or GitLab organization with continuous integration, automated test suites, and weekly staging demonstrations—delivering working, audited software at every sprint milestone.
Measured Economic Impact
Consolidating fragmented operations into custom, purpose-built software generates compounding economic returns across operational, financial, and strategic dimensions. Organizations eliminate between seventy and eighty-five percent of manual administrative data entry, accelerating order-to-cash velocity and contract turnaround from days to minutes. By owning the underlying intellectual property rather than renting generic software seats, enterprises permanently eliminate recurring per-seat SaaS licensing inflation, reducing long-term technology overhead by thirty to fifty percent over a three-year lifecycle. Most importantly, bespoke software creates an insurmountable operational moat: proprietary workflows, automated quality controls, and real-time operational telemetry enable companies to scale transaction volume and revenue exponentially without requiring linear headcount expansion.
Governance & IP Custody
We reject black-box development and vendor lock-in through radical technical governance and transparent code custody. From day one, all development occurs inside your own corporate cloud tenancies (AWS, GCP, or Azure) and version control repositories. We execute a mutual non-disclosure agreement prior to architectural discovery, provide transparent fixed-price sprint quotes with explicit acceptance criteria, and demo testable software releases every single week on isolated staging environments. Upon production release, complete intellectual property ownership—including all application source code, automated CI/CD deployment pipelines, infrastructure-as-code manifests, database migration scripts, and operational disaster recovery runbooks—is unconditionally transferred to your organization with zero proprietary licensing encumbrances.
Engineering Architecture
Core Technical Blueprints & Subsystems
Every system is modularized into isolated subsystems with strict interface contracts and automated testing.
Core Relational State Machine & Business Invariant Engine
Deterministic operational workflows with strict ACID transaction guarantees
At the core of every high-volume operational platform is a deterministic state machine that governs the lifecycle of business entities—whether managing contract lifecycles, complex multi-party fulfillment, dynamic asset scheduling, or multi-currency financial settlements. We engineer robust domain models backed by PostgreSQL relational databases utilizing strict table constraints, custom PostgreSQL domain types, foreign key integrity rails, and serialized transactional isolation. Every status mutation (such as transitioning an operational job from pending dispatch to active execution) is guarded by deterministic state transition validators that prevent invalid state bypasses. High-concurrency operations utilize optimistic concurrency control via row-version tracking or distributed Redis locks with automatic TTL expiration to prevent double-allocation anomalies, race conditions, and ledger variance under peak operational loads.
Code & Schema Deliverables:
- Complete PostgreSQL relational schema with comprehensive foreign key constraints and audit triggers
- Deterministic state transition engine with strict pre-condition and post-condition validator hooks
- Automated database migration pipelines managed via Prisma or Kysely with zero-downtime rollback capabilities
- Optimistic locking and distributed locking abstraction layer for high-concurrency race condition prevention
Failure Modes Prevented:
- ✕Race conditions causing duplicate inventory reservation or concurrent double-booking of field assets
- ✕Partial database writes during network interruptions resulting in orphaned or corrupted transactional records
- ✕Invalid manual status transitions bypassing mandatory operational approvals or compliance gates
- ✕Database deadlocks under concurrent multi-user writes through deterministic locking order patterns
Tech Stack
Fine-Grained Role-Based Access Control (RBAC) & Security Perimeter
Zero-trust organizational security, field-level sanitization, and immutable audit logs
Enterprise operations demand granular security perimeters that balance operational productivity with absolute data privacy. We architect multi-tier role-based access control (RBAC) and attribute-based access control (ABAC) layers that enforce principle of least privilege across internal employees, department supervisors, executive leadership, external field contractors, and third-party compliance auditors. Authentication integrates seamlessly with enterprise Single Sign-On (SSO) providers using OpenID Connect (OIDC), SAML 2.0, Okta, or Google Workspace with mandatory multi-factor authentication (MFA) and cryptographic session revocation. Sensitive data attributes—such as tax identification numbers, proprietary pricing formulas, and customer personal identifiable information (PII)—are protected using field-level application encryption with keys managed via AWS KMS or HashiCorp Vault. Every state modification, login event, and permission escalation is committed to immutable, tamper-evident audit tables with authenticated operator IDs, UTC timestamps, IP geolocations, and full JSON state diffs.
Code & Schema Deliverables:
- Enterprise authentication integration supporting SAML 2.0, OpenID Connect, and granular MFA policies
- Hierarchical RBAC/ABAC authorization middleware enforcing route and entity-level permission boundaries
- Field-level encryption service utilizing envelope encryption with automated key rotation in cloud KMS
- Immutable append-only audit logging pipeline capturing complete cryptographic state mutation diffs
Failure Modes Prevented:
- ✕Privilege escalation attacks where junior staff inadvertently access executive payroll or margin data
- ✕Horizontal data leaks in multi-tenant environments where one business client views another client's data
- ✕Unaccountable data alterations or unauthorized deletions due to missing tamper-evident operator trails
- ✕Session hijacking vulnerabilities eliminated through short-lived access tokens and sliding refresh token rotation
Tech Stack
Resilient Asynchronous Event Engine & External Rail Integrations
Decoupled background processing, reliable webhook ingestion, and resilient API bridges
Modern enterprise platforms must communicate reliably with external banking rails, shipping carriers, government tax portals, CRM systems, and legacy ERP databases without allowing third-party latency to degrade user interface responsiveness. We architect decoupled, asynchronous event-driven pipelines utilizing robust message brokers such as Redis BullMQ, RabbitMQ, or Apache Kafka. Incoming webhooks from payment gateways and logistics partners are immediately ingested into durable staging queues with cryptographic HMAC signature verification and millisecond acknowledgment. Dedicated background workers process events asynchronously with automated exponential backoff retry algorithms, dead-letter queues (DLQ) for malformed payloads, and strict idempotency key tracking to guarantee exact-once processing semantics. Circuit breaker patterns automatically protect your application from cascading failures when third-party partner APIs experience regional outages or degraded performance.
Code & Schema Deliverables:
- Durable background task processing pipeline with multi-queue priority routing and concurrency control
- Cryptographically verified webhook ingestion endpoints with automated deduplication and replay protection
- Dead-letter queue (DLQ) management architecture with automated alerting and manual inspection consoles
- Outbound API integration layer implementing circuit breakers, rate limiting, and exponential retry backoff
Failure Modes Prevented:
- ✕Web application thread pool starvation caused by synchronous third-party HTTP timeouts and slow responses
- ✕Duplicate transaction processing caused by repeated payment gateway webhooks during network retries
- ✕Silent event loss during downstream database maintenance mitigated through persistent durable message queues
- ✕Cascading microservice failure loops prevented through automated circuit breaker tripping and health checks
Tech Stack
High-Performance Analytics Pipeline & Executive Command Console
Sub-second operational telemetry, materialized reporting views, and automated exports
Operational leadership requires instantaneous visibility into company KPIs—such as real-time job cycle times, gross profit margin realizations, inventory stock turn rates, and technician capacity utilization—without waiting for slow end-of-month manual reporting. We build high-speed analytics architectures that segregate analytical query loads from transactional write databases, ensuring heavy reporting queries never slow down front-line staff operations. Transactional events continuously refresh optimized materialized views, columnar storage engines (such as ClickHouse or AWS Athena), or dedicated read-replicas. The user-facing executive command console renders interactive visualizations, custom date range aggregations, and cohort trend analyses with sub-second query response times. Automated reporting workers generate scheduled PDF executive briefs and formatted Excel/CSV data exports delivered directly to stakeholder email inboxes or cloud storage buckets.
Code & Schema Deliverables:
- Segregated analytical reporting architecture utilizing database read-replicas and materialized view pipelines
- Sub-second interactive executive analytics dashboard with customizable KPI metric widgets and filters
- Automated headless background worker for generating formatted PDF summaries and Excel operational reports
- Real-time operational status broadcaster utilizing WebSockets or Server-Sent Events (SSE) for dispatch boards
Failure Modes Prevented:
- ✕Operational UI lockup caused by analytical SQL queries locking critical production database tables
- ✕Executive decision paralysis resulting from days of delay while waiting for manual spreadsheet compilation
- ✕Inconsistent KPI reporting across departments eliminated through standardized centralized data dictionary formulas
- ✕Unmonitored operational bottlenecks enabled by real-time threshold alerts and automated exception notifications
Tech Stack
Engineering Governance
Engineering Standards, QA & Security Protocols
Rigorous development disciplines that protect your code quality, deployment velocity, and infrastructure security.
Strict Type Safety & Enterprise Linting Standards
Code Craftsmanship & Static VerificationAll codebase assets are authored in TypeScript with strict null checks, no implicit any allowances, and deterministic schema validation via Zod. We enforce automated ESLint rules, Prettier formatting pipelines, and SonarQube static code quality gates in CI.
Tooling & Rails
Three-Tier Automated Test Verification
Automated Testing PyramidEvery pull request must pass a comprehensive automated testing battery: fast unit tests for business calculation invariants, integration tests verifying database transactions and repository methods against ephemeral Docker containers, and end-to-end Playwright tests verifying critical user workflows.
Tooling & Rails
Trunk-Based Development & Blue/Green Deployments
Continuous Delivery & Zero-Downtime ReleasesWe implement trunk-based development with short-lived feature branches and automated preview staging environments generated on every pull request. Production releases execute via blue/green deployment orchestration or rolling container updates with automated health check rollback gates.
Tooling & Rails
Zero-Trust Infrastructure & Secret Minimization
Security Hardening & Secret HygieneHardcoded credentials and environmental secrets in code repositories are strictly blocked via automated pre-commit secret scanners. Production secrets are injected at runtime via cloud Key Management Services. Container images undergo automated CVE dependency vulnerability scanning.
Tooling & Rails
Production Case Evidence
Detailed Architecture Problem-Solution Blueprints
Real-world engineering case blueprints detailing baseline bottlenecks, technical intervention, and verified production metrics.
Operational Bottleneck & Root Cause
The company was operating forty dispatch vehicles across regional distribution hubs using whiteboard schedules, driver phone calls, and manual carbon-copy paper delivery manifests. Invoicing was delayed by fifteen days while paper tickets were physically transported to accounting, causing severe cash flow constriction.
Root Cause: Complete lack of centralized operational software: dispatchers had no real-time visibility into vehicle locations or job statuses, and driver route updates were communicated exclusively through uncontrolled phone calls.
Engineered Architecture
We engineered a centralized logistics dispatch web application and progressive mobile field app featuring real-time GPS tracking, automated dynamic route allocation based on driver proximity, and instant digital proof-of-delivery (e-POD) with signature and photo capture. Ingestion pipelines automatically generate electronic invoices in their accounting system upon driver job completion.
Measured Result
Order-to-invoice cycle accelerated from fifteen days to under four minutes, empty fleet mileage decreased by nineteen percent, and annual operational fuel expenses fell by $84,000 within the first six months.
Operational Bottleneck & Root Cause
Monthly client billing required three senior financial controllers to manually cross-reference transaction statements across four banking portals and internal recovery spreadsheets. Billing reconciliation backlogs caused sixty-day invoicing delays and over $120,000 in uncollected quarterly service fees.
Root Cause: Data silos and lack of automated reconciliation logic: fee schedules varied dynamically based on client recovery tiers, and existing accounting software could not handle multi-tiered conditional fee algorithms.
Engineered Architecture
We built an enterprise billing engine with automated bank statement ingestion (MT940 and API feeds), an automated three-way transaction matching queue, configurable tiered commission engines, and an immutable audit trail with role-based sign-off gates.
Measured Result
Reconciliation cycle reduced from three weeks to twenty-two minutes, unbilled fee leakages dropped to zero, and external financial audit preparation time was reduced by seventy-five percent.
Operational Bottleneck & Root Cause
Clinical support coordinators spent an average of four hours per patient manually validating equipment calibration logs, patient clinical compliance notes, and insurance pre-authorization paperwork stored across encrypted email attachments and network folders.
Root Cause: Rigid legacy electronic medical records (EMR) lacked secure patient-facing workflow portals and automated calibration telemetry ingestion endpoints.
Engineered Architecture
We architected a HIPAA-compliant clinical coordination portal featuring zero-trust role isolation, direct IoT telemetry ingestion from diagnostic devices, bidirectional HL7 FHIR bridges to hospital EMRs, and automated insurance compliance packet generation.
Measured Result
Patient onboarding velocity accelerated by sixty-four percent, compliance documentation errors dropped by ninety-one percent, and the platform passed independent SOC 2 Type II and HIPAA security audits with zero remediation findings.
Operational Bottleneck & Root Cause
During high-traffic holiday marketing campaigns, the retailer experienced server crashes, cart abandonment rates exceeding seventy-eight percent, and frequent inventory overselling that resulted in hundreds of canceled customer orders and damaged brand reputation.
Root Cause: Monolithic legacy ecommerce platform with tightly coupled database queries, unoptimized server-side rendering, and slow synchronous inventory lock calls across multiple physical warehouses.
Engineered Architecture
We completely re-architected the ecommerce infrastructure into a high-speed headless storefront using Next.js on edge CDNs, decoupled Shopify Storefront APIs, an asynchronous inventory reservation queue backed by Redis, and streamlined one-page checkout.
Measured Result
Mobile checkout conversion rate increased by forty-two percent, average page load time plummeted from 4.6 seconds to 640 milliseconds, and the infrastructure supported over 12,000 concurrent shoppers during peak sales with zero downtime or oversell incidents.
Sprint Delivery Cadence
Phased Sprint Roadmap & Quality Gates
Predictable milestone delivery with working software demoed every week in your repository.
Phase 1: Architecture Blueprint & Technical Discovery
Domain Modeling, Security Threat Assessment & Prototype Schema
Deliverables:
- Complete written Software Architecture Document (SAD) and system context diagrams
- Comprehensive PostgreSQL database entity schema and domain invariant specifications
- Security threat model identifying authentication boundaries, RBAC matrices, and compliance scopes
- Granular sprint delivery backlog with fixed pricing quotes and milestone acceptance criteria
Gate Criteria
Formal architectural sign-off by your technical and commercial stakeholders with mutual discovery fee credited toward construction.
Phase 2: Core Platform Engine & Relational Backbone
State Machines, Authentication Security & Primary CRUD Workflows
Deliverables:
- Operational database deployment with automated schema migrations in your cloud tenancy
- Enterprise SSO and RBAC authentication layer with granular permission middleware
- Primary business entity state machine and core operational workflow screens
- Weekly functional staging deployment demonstrated live every Friday with your team
Gate Criteria
Demonstration of core end-to-end data lifecycle in staging environment with automated unit test suite passing in CI.
Phase 3: Asynchronous Integrations & Advanced Automation
External API Rails, Background Worker Queues & Reporting
Deliverables:
- Resilient webhook ingestion pipelines with dead-letter queue exception management
- Third-party external API connectors (payment gateways, ERPs, CRM systems, hardware telematics)
- Real-time analytics dashboard with sub-second query performance and export workers
- Automated integration and regression test suites verifying edge case failure modes
Gate Criteria
Successful end-to-end integration sandbox testing across all external partners with simulated network failure resilience.
Phase 4: Security Hardening, Production Cutover & Handover
Penetration Testing, Staff Walkthroughs & Unconditional IP Assignment
Deliverables:
- Third-party dependency security audit and vulnerability penetration test reports
- Comprehensive operational runbooks detailing database backup, restore, and scaling procedures
- Recorded video staff training sessions and technical administrator documentation
- Executed Intellectual Property Assignment Certificate transferring 100% code ownership
Gate Criteria
Zero critical or high security vulnerabilities, successful zero-downtime production deployment, and signed client acceptance certificate.
Financial Transparency
Total Cost of Ownership & Risk Mitigation
Understand the core technical variables that dictate development investment and long-term operating costs.
Per-Seat SaaS Licensing vs Capitalized IP Asset
TCO VariablePrimary Cost Driver
Commercial SaaS vendors charge compounding monthly fees per user seat, plugin fees, and tiered transaction overage charges that scale aggressively as company headcount increases.
Risk Without Proper Architecture
Operating expenses compound unpredictably, creating perverse incentives to restrict employee software access or share insecure master credentials.
Our Engineering Mitigation
Custom software is a capitalized corporate balance sheet asset with zero per-seat fees, allowing you to grant role-restricted access to unlimited employees, contractors, and clients without incremental software licensing cost.
Database Schema Design & Query Concurrency Scaling
TCO VariablePrimary Cost Driver
Transactional databases that lack proper indexing, normalization, foreign key constraints, or connection pooling degrade precipitously when concurrent user count exceeds baseline projections.
Risk Without Proper Architecture
Slow database queries cause cascading application thread pool exhaustion, 504 gateway timeout errors during peak business hours, and catastrophic operational downtime.
Our Engineering Mitigation
We architect optimized relational schemas with covering composite indexes, strict query execution budgets (< 50ms), connection pooling via PgBouncer, and segregated read-replicas for heavy analytical reporting.
Third-Party Integration Fragility & API Churn
TCO VariablePrimary Cost Driver
Modern applications depend on external cloud APIs for credit card processing, mapping, SMS messaging, and accounting sync. External vendors frequently deprecate legacy endpoints or experience regional outages.
Risk Without Proper Architecture
Direct synchronous API dependencies cause your entire application to crash or freeze when an external partner experiences intermittent network latency or rate limit throttling.
Our Engineering Mitigation
We isolate all external communications behind resilient asynchronous message queues with exponential backoff retries, idempotent deduplication, circuit breakers, and comprehensive dead-letter queue monitoring.
Technical Debt Accumulation & Maintenance Overhead
TCO VariablePrimary Cost Driver
Quickly hacked codebases built without strict typing, automated test suites, or clear modular boundaries require exponential engineering hours to patch, debug, and enhance over time.
Risk Without Proper Architecture
Software velocity grinds to a halt after eighteen months as engineers fear that changing one module will inadvertently break three unrelated business workflows.
Our Engineering Mitigation
We enforce strict TypeScript typing, modular domain boundaries, automated regression test suites in CI, and thorough documentation runbooks that ensure internal developers or future teams can maintain and extend the software effortlessly.
Results
What This Service Delivers
Outcome 1
One login for staff with roles and an audit trail
Staff log into one system where every record carries an owner and a history — no more reconciling five sheets on a Friday.
Outcome 2
Modules shipped in payback order while the business keeps running
The highest-payback module ships first, so the business feels relief in weeks while later modules build on proven ground.
Outcome 3
Docs, tests and access lists your team keeps
Tests, docs and access lists live in your repo — any competent team can extend the platform without us.
Fit Check
Is This Service Right for Your Business?
When It Fits
You run repeatable operations — bookings, jobs, inventory, billing — across sheets, email and people, and need one system with roles and an audit trail.
✕When It Doesn't
You need a simple brochure site or a mobile-only app with no shared backend — a smaller website or app engagement fits better.
Use Cases
Business Use Cases We Serve
Bookings & scheduling ops
Calendars, slots and confirmations currently spread across calls, sheets and memory — moved into one bookable system.
Jobs & inventory tracking
Stock, jobs and statuses updated by different people in different files — unified with role-based editing.
Billing & reconciliation
Invoices, retries and matching done by hand each month — automated with an audit trail.
Gallery
What Typical Deliverables Look Like
Sample deliverables from a typical engagement — yours follow the same shape, scoped to your business.
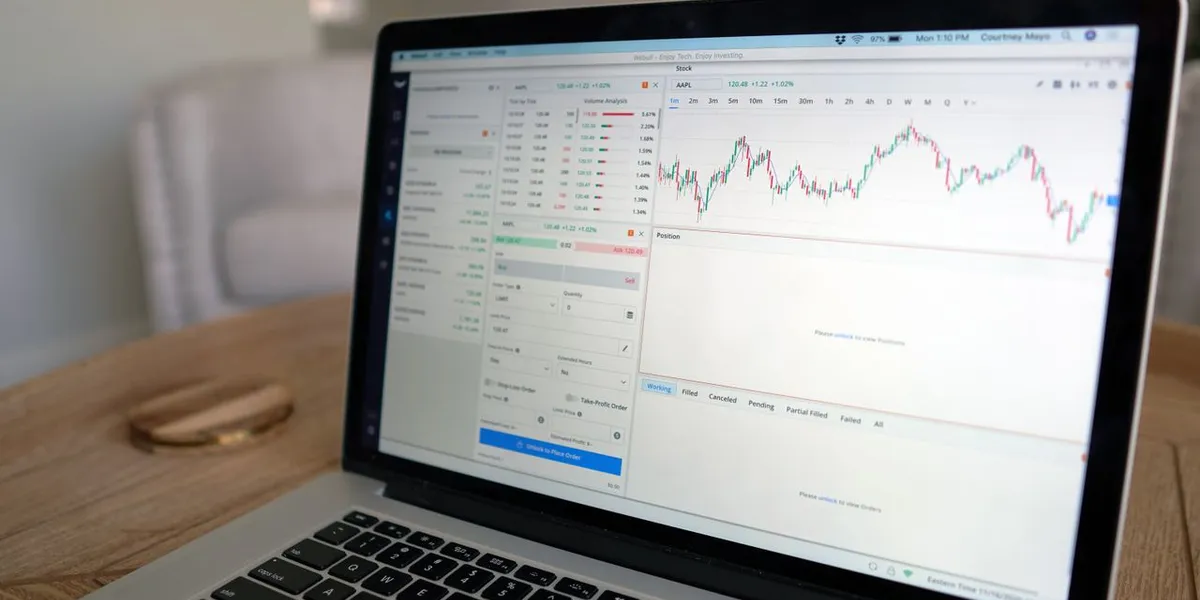
Visual 1
Scoped screens
Clickable mock of the first module — approved before any code is written.
Visual 2
Weekly demo build
Working release in your repo with tests passing and access you control.
Visual 3
Handover pack
Docs, data dictionary and access lists your team keeps on day one.
Timeline
How Long Does custom software Take?
Discovery typically 1–3 weeks; first usable release in weekly sprints after that. The same four delivery stages run every engagement — you approve progress at each gate before the next begins.
Stage 1
Map the workflow
We shadow the process, list every step and handoff, then agree which module pays back first.
Stage 2
Build module one
First working release in weekly sprints — real users click it early, redirecting scope before it hardens.
Stage 3
Expand in order
Remaining modules ship by payback rank, each with tests and a demo you approve.
Stage 4
Handover
Docs, access lists and a walkthrough — then monthly support or a documented exit with everything transferred.
Pricing
What Drives the Cost of custom software?
- 1
Number of modules and user roles in scope
- 2
Integrations with existing tools and data migration volume
- 3
Custom workflows versus standard patterns
Pricing shape: Staged fixed-price phases; stop after any working release.
Indicative ranges live on the pricing page — your fixed quote arrives with the discovery scope.
Process
Delivery Stack and Pricing
Stages shown above — here is what they run on and how they are priced.
Stack & Tools
TypeScriptNext.jsReactNode.jsPython / FastAPIPostgreSQLRedisDockerGraphQL / REST APIsTailwind CSSPrisma / DrizzleGitHub Actions
Pricing Shape
Staged fixed-price phases; stop after any working release.
Due Diligence
Technical Due Diligence FAQs
How much does custom software cost?
After a short paid discovery (typically 1–3 weeks) you receive a fixed price with milestones. Staged fixed-price phases; stop after any working release. Discovery is credited toward the build if you proceed.
How much does custom software cost?
After a short paid discovery you receive a fixed price with milestones — most small-business platforms land in staged phases so you can stop after any working release.
Can you take over our existing system?
Yes, after a code review. We list risks, quick wins and what not to touch, then propose a step-by-step plan that keeps the business running.
How do you handle our current spreadsheets?
We import them as the starting dataset, then replace sheet-by-sheet with validated screens — nothing is retyped from scratch.
What happens after launch?
A handover walkthrough plus monthly support for fixes and small improvements — or your team runs it with our docs.
How long does it take to start?
Discovery starts within days of agreement. Builds run in weekly sprints with a demo every week.
Who owns the work?
You do, under a signed agreement — code, docs and accounts are handed over at the end.
Content last reviewed September 2026.
Straight Talk
Mistakes We Prevent & How We Compare
Common mistakes we prevent
Automating a broken process unchanged — we map and simplify first
Skipping roles and permissions until later — designed in from module one
No data dictionary, so reports disagree — definitions agreed upfront
Us vs the usual alternative
Scope
AnyPlace: Fixed phases you can stop between
Typical alternative: Open-ended hourly with no exit points
Build order
AnyPlace: Module by module, business running
Typical alternative: Big-bang rewrite, months dark
Handover
AnyPlace: Docs, tests and access lists
Typical alternative: Code dump with no context
Before
The starting point we usually find
Operations run on spreadsheets, email threads and memory — mistakes surface at month-end.
After
Where this service leaves you
One platform with roles and audit trails — the same work takes hours, and every number traces to source.
Worth knowing: W3Techs reports that WordPress powers over 40% of the websites it tracks — a reminder that boring, proven stacks run most of the web. Source: W3Techs · Verified September 2026
Related Services
Pairs Well With
Mobile App Development (iOS & Android)
Flutter and native apps tied to your backend — store listing, updates and handover included.
View service→
Data Pipelines & Dashboards
Centralize messy data from multiple tools into dashboards your leadership actually checks weekly.
View service→
Cloud Setup & DevOps
Cloud hosting setup, CI/CD pipelines and cost hygiene on AWS, Azure or GCP — with runbooks your team can follow.
View service→
TELL US ABOUT YOUR PROJECT
Tell Us What to Build, Fix or Modernize
Send a short brief. We reply within 12 hours with clarifying questions and a discovery quote — no retainers, no spam.
What Happens Next
Request a Discovery Quote
Share your goals and timeline. NDA signed first if needed.
12-hour response