Enterprise Cybersecurity Services: Engineered for Resilient Defense
A prioritized fix list, not fear: access review, configuration check and code spot-checks, ranked by risk with effort estimates — so you fix what matters first.
Best for growing businesses in India, the USA, UK, Australia and Canada where staff changed, tools piled up, and nobody has reviewed who can access what — or clients started asking about your security practices. Fixed-price review; fixes scheduled by priority afterwards.
Executive Brief
Strategic Context & Engineering Purpose
How our security review engagements de-risk operational transitions and produce enduring software assets.
Operational Challenge
Modern commercial enterprises and high-growth technology organizations operate across an expanding, distributed attack surface fraught with systemic vulnerabilities. Legacy access credentials left active by departed employees, unencrypted cloud storage buckets, vulnerable third-party open-source software dependencies, misconfigured Single Sign-On (SSO) permissions, and un-sanitized API endpoints expose businesses to devastating ransomware intrusions and catastrophic regulatory penalties under GDPR, CCPA, and industry frameworks. When prospective enterprise buyers issue exhaustive 200-question vendor security assessments, commercial sales pipelines grind to an abrupt halt because engineering teams lack the formal security documentation, penetration test evidence, and continuous compliance posture required to satisfy institutional risk officers.
Architectural Approach
We deliver practical, engineering-driven cybersecurity assessments, penetration testing, and hands-on remediation protocols tailored to real-world operational environments. Rather than producing 100-page generic automated scanner reports filled with false positives, our senior cybersecurity architects perform rigorous manual application penetration testing (OWASP Top 10 and ASVS Level 3), cloud security posture management (CSPM) audits across AWS, GCP, and Azure, and comprehensive identity access governance reviews. We deliver a prioritized, risk-ranked remediation roadmap accompanied by verified code patches, hardened Terraform infrastructure policies, and direct pull requests that eliminate critical vulnerabilities without disrupting production engineering velocity.
Measured Economic Impact
Executing an engineering-first cybersecurity hardening program eliminates over ninety-five percent of exploitable external attack vectors while turning corporate security into a formidable commercial sales asset. Enterprise vendor security questionnaires transition from multi-week deal blockers into rapid 48-hour competitive differentiators, accelerating B2B sales cycles and unlocking seven-figure enterprise contracts. Organizations achieve seamless audit readiness for SOC 2 Type II, ISO 27001, and HIPAA certifications while securing optimal premium rates from corporate cyber insurance underwriters through verifiable cryptographic evidence of continuous defensive controls.
Governance & IP Custody
We reject alarmist scare tactics and maintain absolute transparency and strict operational governance throughout every security engagement. All penetration testing exercises and vulnerability scans operate under mutual, written Rules of Engagement (ROE) designed to guarantee zero disruption to live customer workflows. We author remediation pull requests directly within your private version control repositories and provide complete before-and-after cryptographic verification evidence for every patched finding. Upon project completion, all executive summary reports, detailed technical remediation guides, employee credential audit inventories, and repeatable quarterly self-audit runbooks are handed over with complete ownership.
Engineering Architecture
Core Technical Blueprints & Subsystems
Every system is modularized into isolated subsystems with strict interface contracts and automated testing.
Cloud Security Posture Management (CSPM) & Identity Perimeter Hardening
Multi-cloud configuration auditing, IAM least-privilege enforcement, and network segmentation
Over eighty percent of enterprise cloud data breaches stem from basic configuration oversights and unmanaged identity credentials rather than zero-day software exploits. We execute comprehensive Cloud Security Posture Management audits across AWS, GCP, and Azure tenancies, evaluating cloud assets against the CIS (Center for Internet Security) Benchmarks. We audit every IAM role, policy, and service account, eliminating wildcard permissions and implementing strict principle-of-least-privilege policies. Public access to S3 object buckets and database snapshots is cryptographically blocked, VPC network security groups are hardened with private-only subnet topologies, and multi-factor authentication (MFA) is enforced organization-wide with hardware security key (FIDO2/WebAuthn) support.
Code & Schema Deliverables:
- CIS Benchmark cloud posture audit report covering complete multi-cloud infrastructure and networking
- IAM privilege remediation plan removing unused credentials, wildcard policies, and stale service accounts
- Automated cloud policy-as-code guardrails preventing accidental public exposure of storage or databases
- Single Sign-On (SSO) and mandatory MFA architecture integration with corporate identity providers
Failure Modes Prevented:
- ✕Catastrophic data leaks caused by accidentally making S3 buckets or database snapshots public
- ✕Account compromise resulting from compromised permanent developer IAM access keys committed to Git
- ✕Lateral attacker movement across cloud environments due to unsegmented flat VPC networks
- ✕Session hijacking and credential stuffing attacks mitigated through hardware-backed FIDO2 MFA
Tech Stack
Web Application & API Penetration Testing (OWASP ASVS)
Manual vulnerability exploitation, business logic flaw identification, and API security
Automated vulnerability scanners detect basic syntax flaws but consistently fail to discover complex business logic vulnerabilities, authorization bypasses, and multi-step privilege escalations. Our security engineers conduct rigorous, manual penetration testing guided by the OWASP Application Security Verification Standard (ASVS Level 3) and OWASP API Security Top 10. We test for Broken Object Level Authorization (BOLA/IDOR), multi-tenant data leakage, JWT token forgery, race conditions in financial ledger endpoints, and server-side request forgery (SSRF). Every identified finding is documented with proof-of-concept reproduction scripts, root-cause code analysis, and exact drop-in remediation patches.
Code & Schema Deliverables:
- Manual penetration testing report covering authenticated and unauthenticated application attack surfaces
- Proof-of-concept reproduction scripts and curl commands demonstrating exact vulnerability mechanics
- Prioritized remediation pull requests with drop-in code patches ready for developer review and merge
- Executive summary report formatted specifically for enterprise B2B customer vendor security reviews
Failure Modes Prevented:
- ✕Horizontal privilege escalation (BOLA/IDOR) allowing one customer to view another customer's private data
- ✕Remote code execution or cloud credential harvesting via Server-Side Request Forgery (SSRF) vulnerabilities
- ✕Business logic exploitation allowing malicious users to bypass payment gates or tamper with pricing variables
- ✕Database compromise through sophisticated blind SQL injection or NoSQL parameter tampering
Tech Stack
Automated DevSecOps Pipeline: SAST, DAST & Dependency Vulnerability Remediation
Shift-left automated code scanning, software bill of materials (SBOM), and container signing
Maintaining a secure software application requires embedding security checks directly into daily engineering workflows rather than treating security as an afterthought. We design and integrate automated DevSecOps pipelines into your GitHub Actions or GitLab CI workflows. Static Application Security Testing (SAST) tools scan every pull request for hardcoded secrets, unsafe memory operations, and vulnerable coding patterns before code merges. Software Bill of Materials (SBOM) generators and dependency scanners (Snyk, Dependabot, Trivy) continuously monitor your open-source libraries against the National Vulnerability Database (NVD). Container images are scanned for OS-level vulnerabilities and cryptographically signed using Sigstore Cosign before promotion to production registries.
Code & Schema Deliverables:
- Automated SAST and secret-detection pipeline scanning pull requests to prevent hardcoded credentials
- Software Bill of Materials (SBOM) generation pipeline tracking all open-source libraries and licenses
- Container image security scanning with automated build-breaking thresholds for critical CVEs
- Cryptographic image signing pipeline utilizing Sigstore Cosign to guarantee container provenance
Failure Modes Prevented:
- ✕Production deployment of open-source packages containing known critical remote code execution vulnerabilities
- ✕Accidental leakage of production database passwords, API keys, or private SSH certificates into Git history
- ✕Software supply chain attacks resulting from unauthorized container image tampering in registries
- ✕Legal liabilities and licensing violations arising from un-approved copyleft open-source libraries
Tech Stack
Zero-Trust Cryptographic Hygiene & Immutable Audit Telemetry
Envelope encryption, KMS key custody, tamper-evident audit trails, and incident logging
Enterprise security architecture requires assuming that network perimeters will eventually be breached and engineering data layers that remain resilient even under compromise. We implement zero-trust data protection architectures utilizing envelope encryption and cloud hardware security modules (AWS KMS, Azure Key Vault, or HashiCorp Vault). Sensitive customer data attributes—including tax identifiers, banking details, and healthcare records—are encrypted at the application layer with unique data encryption keys (DEKs) before touching storage disks. All authentication events, administrative permission elevations, and data access requests are streamed to an immutable, append-only security information and event management (SIEM) pipeline with tamper-evident cryptographic hashing.
Code & Schema Deliverables:
- Application-layer envelope encryption service integrated with cloud Hardware Security Modules (HSM)
- Automated KMS cryptographic key management policy with scheduled annual key rotation
- Immutable append-only audit logging pipeline streaming security events to an isolated log repository
- SIEM alerting rules detecting brute-force credential attacks, abnormal geographic logins, and data exfiltration
Failure Modes Prevented:
- ✕Mass customer data exposure in the event of a raw database snapshot theft or unauthorized backup access
- ✕Cryptographic key compromise due to static, un-rotated encryption keys stored in application configuration files
- ✕Attacker log tampering or deletion designed to conceal unauthorized lateral movement during an intrusion
- ✕Delayed breach detection allowing unauthorized adversaries to persist undetected within corporate networks
Tech Stack
Engineering Governance
Engineering Standards, QA & Security Protocols
Rigorous development disciplines that protect your code quality, deployment velocity, and infrastructure security.
OWASP ASVS Level 3 & API Security Top 10 Verification
Application SecurityAll web and mobile application endpoints are audited against the OWASP Application Security Verification Standard (ASVS Level 3). Verification validates authentication strength, cryptographic session management, access control boundaries, and input sanitization.
Tooling & Rails
Cryptographic Envelope Hygiene & Hardware KMS Key Custody
Data ProtectionAll sensitive data attributes are encrypted using AES-256-GCM envelope encryption with master keys hosted in FIPS 140-2 Level 3 Hardware Security Modules (AWS KMS / Azure Key Vault). Master keys are configured with automated annual key rotation policies.
Tooling & Rails
Secure Software Supply Chain Integrity (SLSA Level 3)
DevSecOpsAll application source code dependencies are monitored continuously via automated SBOM analysis. Pull requests with high or critical CVE vulnerabilities are blocked automatically. Production Docker container images are cryptographically signed using Sigstore Cosign.
Tooling & Rails
Continuous Cloud Security Posture Management (CSPM)
Cloud GovernanceCloud environments are evaluated continuously against the CIS Benchmarks and AWS Foundational Security Best Practices. Any unapproved drift—such as an open security group port or un-encrypted disk volume—triggers real-time security alerts.
Tooling & Rails
Production Case Evidence
Detailed Architecture Problem-Solution Blueprints
Real-world engineering case blueprints detailing baseline bottlenecks, technical intervention, and verified production metrics.
Operational Bottleneck & Root Cause
A Tier-1 prospective enterprise client blocked a $450K annual contract after identifying broken authorization flaws and missing encryption in their vendor security audit.
Root Cause: Broken Object Level Authorization (BOLA) in API routes allowing authenticated users to modify URL parameters to access employee payroll records from other companies.
Engineered Architecture
Executed comprehensive API penetration testing, implemented PostgreSQL Row-Level Security (RLS) policies enforcing multi-tenant isolation, and added envelope encryption.
Measured Result
Eliminated all authorization vulnerabilities; passed the enterprise customer's re-audit with zero findings; closed the $450K annual subscription.
Operational Bottleneck & Root Cause
The client suffered from credential stuffing attacks and automated bot account creation that degraded server performance and triggered fraud investigation alerts.
Root Cause: Public authentication endpoints lacked rate limiting, IP reputation filtering, and device fingerprinting, enabling distributed credential stuffing scripts.
Engineered Architecture
Implemented Cloudflare Enterprise WAF bot management, sliding window Redis rate limiting, and password breach checking against HaveIBeenPwned database.
Measured Result
Bot account creation dropped by 99.8%; zero fraudulent account takeovers across 600,000 active users; customer support fraud inquiries reduced by 92%.
Operational Bottleneck & Root Cause
The organization was preparing for a mandatory HIPAA and HITRUST compliance audit but lacked formal access review procedures, data encryption keys, and audit logs.
Root Cause: Organic cloud growth over five years resulting in shared administrative root logins, un-encrypted S3 file backups, and un-tracked employee access permissions.
Engineered Architecture
Implemented AWS Control Tower multi-account landing zones, migrated identity management to Okta with mandatory FIDO2 MFA, and encrypted all storage with KMS.
Measured Result
Achieved 100% clean HIPAA third-party compliance certification in 60 days; successfully onboarded three major regional hospital health systems.
Operational Bottleneck & Root Cause
The development team was overwhelmed by a 200-page automated vulnerability scanner report containing 1,400 'vulnerabilities', unable to determine what was real.
Root Cause: Over-reliance on noisy automated scanners that flagged theoretical library warnings without evaluating runtime exploitability or business context.
Engineered Architecture
Conducted manual vulnerability triaging, filtering out 1,350 false positives, and authored direct code remediation pull requests for the 18 genuine high-risk flaws.
Measured Result
Remediated all 18 genuine security vulnerabilities in two weeks; unblocked engineering roadmap while providing verified audit evidence for enterprise buyers.
Sprint Delivery Cadence
Phased Sprint Roadmap & Quality Gates
Predictable milestone delivery with working software demoed every week in your repository.
Phase 01: Attack Surface Discovery, Rules of Engagement & Cloud Audit
Asset mapping, cloud configuration benchmarking, and threat boundary modeling
Deliverables:
- Mutual Rules of Engagement (ROE) document defining authorized testing windows and boundaries
- Comprehensive attack surface discovery map cataloging all public IP ranges, domains, and APIs
- Cloud Security Posture Management (CSPM) audit evaluating AWS/GCP tenancies against CIS Benchmarks
- Identity and credential inventory cataloging all active employees, service accounts, and API keys
Gate Criteria
Mutual sign-off on Rules of Engagement and completed cloud configuration security audit.
Phase 02: Manual Application & API Penetration Testing
Vulnerability exploitation, authorization testing, business logic flaws, and proof of concepts
Deliverables:
- Manual penetration testing covering OWASP Top 10, ASVS Level 3, and API security vulnerabilities
- Detailed proof-of-concept exploit scripts and reproduction instructions for every validated finding
- Business logic flaw analysis evaluating multi-tenant data isolation and financial authorization gates
- Weekly security briefing summarizing critical findings with immediate interim mitigation steps
Gate Criteria
Completed penetration testing execution across all scoped web, mobile, and API endpoints.
Phase 03: Hands-On Remediation, Code Patches & DevSecOps Automation
Direct code patches, Terraform policy hardening, automated CI security gates, and re-testing
Deliverables:
- Production-ready code remediation pull requests addressing all identified application vulnerabilities
- Hardened Terraform infrastructure-as-code manifests enforcing least privilege and encryption
- Automated DevSecOps pipeline integration (SAST, secret detection, container scanning) in GitHub Actions
- Comprehensive re-testing validation certifying that all identified vulnerabilities have been eliminated
Gate Criteria
Verification that 100% of critical and high-severity vulnerabilities are successfully remediated and verified.
Phase 04: Executive Attestation, Compliance Evidence & Quarterly Runbook
Formal attestation reports, vendor questionnaire packages, and repeatable self-audit runbooks
Deliverables:
- Formal third-party penetration testing summary report signed by senior security architects
- Enterprise vendor security assessment evidence package for accelerating enterprise B2B sales
- Repeatable quarterly security self-audit checklist and runbook for internal engineering teams
- Executive security briefing for board members, enterprise leadership, and insurance underwriters
Gate Criteria
Delivery of final signed security attestation package, repeatable runbook walkthrough, and full IP handover.
Financial Transparency
Total Cost of Ownership & Risk Mitigation
Understand the core technical variables that dictate development investment and long-term operating costs.
Proactive Hardening vs Catastrophic Ransomware & Breach Costs
TCO VariablePrimary Cost Driver
The average cost of a corporate data breach exceeds $4.4 million according to IBM Security telemetry, including incident response, legal fees, and brand damage.
Risk Without Proper Architecture
Unpatched vulnerabilities and weak credential hygiene leave companies vulnerable to devastating ransomware intrusions that paralyze operations.
Our Engineering Mitigation
We eliminate 95%+ of external exploit vectors through rigorous penetration testing and identity hardening, protecting corporate continuity and enterprise valuation.
Enterprise Deal Velocity vs Security Review Bottlenecks
TCO VariablePrimary Cost Driver
B2B enterprise buyers mandate comprehensive vendor security assessments, third-party penetration tests, and SOC 2 compliance before signing contracts.
Risk Without Proper Architecture
Failing enterprise security audits or delaying responses by weeks causes high-value six-figure deals to stall and slip away to competitors.
Our Engineering Mitigation
We provide clean third-party security attestation reports and pre-filled questionnaire evidence, accelerating enterprise procurement approval to 48 hours.
Engineering-First Fixes vs Noisy Automated Scanner Retainers
TCO VariablePrimary Cost Driver
Traditional security firms charge expensive retainers simply to deliver 200-page automated tool outputs filled with false positives that developers ignore.
Risk Without Proper Architecture
Engineering teams waste hundreds of hours chasing false alarms while genuine critical vulnerabilities remain unpatched in production code.
Our Engineering Mitigation
We eliminate false positives through manual verification and provide drop-in code pull requests, fixing root-cause vulnerabilities in days.
Verifiable Defensive Controls vs Cyber Insurance Premiums
TCO VariablePrimary Cost Driver
Cyber liability insurance underwriters have dramatically tightened underwriting requirements, denying coverage or hiking premiums for firms without verified controls.
Risk Without Proper Architecture
Failing to demonstrate mandatory MFA, immutable backups, and regular penetration testing results in policy cancellation or denied claims after incidents.
Our Engineering Mitigation
Our cryptographic evidence packages satisfy underwriter requirements, securing optimal insurance coverage rates and peace of mind.
Results
What This Service Delivers
Outcome 1
An access list that is current and owned
Every login, key and share listed with a named owner — leavers revoked, shared logins split, evidence filed.
Outcome 2
A risk-ranked fix plan with effort estimates
Findings ordered by risk with effort estimates, so the first fixes are the ones that matter most.
Outcome 3
A quarterly re-check checklist your team can run
A quarterly re-check list your team runs in an afternoon — security stays current without another engagement.
Fit Check
Is This Service Right for Your Business?
When It Fits
Staff changed, tools piled up, and nobody has reviewed who can access what — or clients started asking about your security practices.
✕When It Doesn't
You need certified penetration testing or compliance attestation for a regulator — that requires an accredited auditor, which we are not.
Use Cases
Business Use Cases We Serve
Post-turnover cleanup
People left, accounts stayed — every login, key and share reviewed and reassigned or revoked.
Client questionnaire
A buyer asks how you handle security — we produce the review, fixes and evidence trail to answer.
Pre-launch hardening
New system about to go live — configs, secrets and dependencies checked before exposure.
Gallery
What Typical Deliverables Look Like
Sample deliverables from a typical engagement — yours follow the same shape, scoped to your business.
Visual 1
Access inventory
Every login, key and share listed with a named owner.
Visual 2
Ranked findings
Issues ordered by risk with effort estimates attached.
Visual 3
Fix evidence
Before/after records for each fix auditors can verify.
Timeline
How Long Does security review Take?
Review typically 1–2 weeks, fixes scheduled by priority after that. The same four delivery stages run every engagement — you approve progress at each gate before the next begins.
Stage 1
Inventory access
Every account, key, share and admin role listed with an owner.
Stage 2
Review configs
Hosting, DNS, backups and app settings checked against a written checklist.
Stage 3
Spot-check code
Auth, inputs and secrets handling reviewed where risk is highest.
Stage 4
Report and fix
Ranked fixes with effort; quick wins implemented, rest scheduled.
Pricing
What Drives the Cost of security review?
- 1
Number of accounts, apps and integrations to review
- 2
Depth of code spot-checks requested
- 3
Remediation scope included versus report-only
Pricing shape: Fixed-price review; fixes scheduled by priority afterwards.
Indicative ranges live on the pricing page — your fixed quote arrives with the discovery scope.
Process
Delivery Stack and Pricing
Stages shown above — here is what they run on and how they are priced.
Stack & Tools
Wazuh / OSSECOWASP ZAPSnykTrivyHashiCorp VaultSonarQubeSemgrepOpenSSLCloudflare WAFAWS GuardDutyWireGuardBurp Suite
Pricing Shape
Fixed-price review; fixes scheduled by priority afterwards.
Due Diligence
Technical Due Diligence FAQs
How much does security review cost?
After a short paid discovery (typically 1–3 weeks) you receive a fixed price with milestones. Fixed-price review; fixes scheduled by priority afterwards. Discovery is credited toward the build if you proceed.
What is the difference between an automated vulnerability scan and a manual penetration test?
Automated vulnerability scanners rely on pre-configured scripts and signatures to check for known software versions and common syntax errors. While valuable for basic hygiene, automated scanners produce enormous volumes of false positives and are fundamentally incapable of detecting complex business logic flaws, authorization bypasses (such as BOLA/IDOR), or multi-step privilege escalation paths. Manual penetration testing involves experienced ethical hackers actively probing your application logic, manipulating API payloads, attempting credential forgery, and chaining multiple minor vulnerabilities to achieve unauthorized access. Our assessments combine automated baseline scanning with deep manual penetration testing, delivering actionable, verified findings accompanied by exact code remediation patches.
Will a penetration test or security audit cause downtime or disrupt our live customer users?
No. All penetration testing and security reviews are governed by a mutually agreed, written Rules of Engagement (ROE) document established prior to testing. We typically conduct penetration tests against dedicated, production-mirror staging environments seeded with synthetic data to completely eliminate operational risk. If testing must occur against production environments, our security engineers coordinate testing during low-traffic maintenance windows, utilize rate-limited testing tools to prevent denial-of-service conditions, and immediately halt any test if unexpected latency or system alerts are observed.
How do you help our company answer complex enterprise vendor security questionnaires?
Enterprise vendor security questionnaires (such as SIG, CAIQ, or custom 200-question Excel spreadsheets) routinely delay B2B sales cycles by weeks. Following our security review and hardening engagement, we provide an Enterprise Security Evidence Package. This package includes an executive penetration testing summary report signed by our senior security architects, architectural network diagrams, data encryption specifications, incident response runbooks, and a pre-compiled master response sheet addressing common enterprise security questions regarding access controls, data retention, encryption standards, and employee background checks. This allows your sales team to complete questionnaires in under 48 hours with verified proof.
What is BOLA / IDOR, and why is it considered the most dangerous API security vulnerability?
Broken Object Level Authorization (BOLA), historically known as Insecure Direct Object Reference (IDOR), occurs when an API endpoint accepts an object identifier (such as an account number, invoice ID, or user UUID) in a request and retrieves the corresponding database record without verifying whether the authenticated user actually has permission to view that specific record. For example, an attacker logs into their own account (ID 105) and modifies an API URL to request data for ID 106, receiving another customer's private financial data. BOLA is the number-one vulnerability in modern APIs because automated scanners cannot understand business permission boundaries. We eliminate BOLA by implementing database Row-Level Security (RLS) and strict server-side authorization middleware on every API endpoint.
How do you help us prepare for SOC 2 Type II or ISO 27001 certification audits?
Achieving SOC 2 Type II or ISO 27001 certification requires demonstrating continuous adherence to strict security controls over a multi-month observation window. We bridge the gap between abstract compliance requirements and concrete engineering implementation. We configure your cloud landing zone to enforce mandatory MFA, configure automated multi-region encrypted backups, establish immutable CloudTrail audit logging, implement automated dependency vulnerability scanning in your CI/CD pipelines, and author mandatory information security policy documents (including Incident Response, Disaster Recovery, and Change Management policies). We work alongside your compliance automation platform (such as Vanta, Drata, or Secureframe) to ensure all automated evidence tests pass.
What steps do you take to secure our third-party open-source software supply chain?
Modern web applications frequently consist of over eighty percent open-source libraries and NPM/Python packages, creating significant supply chain risk if dependencies contain vulnerabilities or malicious packages. We implement automated Software Bill of Materials (SBOM) generation and continuous dependency scanning using tools like Trivy, Snyk, and Dependabot directly within your pull request workflow. Pull requests that introduce packages with known High or Critical Common Vulnerabilities and Exposures (CVEs) are blocked automatically. Furthermore, we establish internal package lockfile verification and private container registry scanning to ensure only vetted, cryptographically signed container images can deploy to production.
How do you protect sensitive customer personal identifiable information (PII) at rest in the database?
While standard cloud database encryption at rest (such as AWS RDS default storage encryption) protects against physical hard drive theft in data centers, it offers zero protection if an application layer is compromised by SQL injection or credential theft. We implement application-level envelope encryption using AWS KMS or HashiCorp Vault. Sensitive fields (such as Social Security numbers, bank account details, and medical records) are encrypted before reaching the database using individual data encryption keys (DEKs) wrapped by a master key hosted in a Hardware Security Module (HSM). Even if a malicious actor acquires a full raw SQL database export, the sensitive records remain mathematically unreadable ciphertext without KMS decryption access.
What is your approach to Single Sign-On (SSO) and multi-factor authentication (MFA) enforcement?
Passwords alone represent the single greatest credential vulnerability in modern organizations. We eliminate fragmented individual account credentials by implementing centralized Single Sign-On (SSO) integrated with corporate identity providers like Okta, Google Workspace, or Microsoft Azure AD using SAML 2.0 and OpenID Connect (OIDC). We configure organizational policies that mandate multi-factor authentication (MFA) across all corporate systems, prioritizing phishing-resistant hardware security keys (FIDO2 / WebAuthn / YubiKeys) or authenticator apps while deprecating insecure SMS-based verification. In addition, we implement automated user lifecycle provisioning (SCIM) that instantly revokes access across all company tools the moment an employee departs.
Who owns the security reports, code remediation patches, and audit evidence generated during the engagement?
Your organization maintains one hundred percent exclusive ownership of all penetration testing reports, executive summary documentation, vulnerability reproduction scripts, remediation code pull requests, and compliance evidence packages. All findings are treated with the strictest confidentiality and secured in encrypted vaults. We do not retain proprietary rights to any security documentation or remediation code. Upon engagement completion, full intellectual property and all deliverables are transferred directly into your corporate custody.
What repeatable tools or checklists do you provide so our internal team can maintain security post-launch?
Security is an ongoing operational discipline, not a one-time project. At the conclusion of every engagement, we deliver a customized Quarterly Security Self-Audit Runbook tailored to your exact technology stack. This runbook includes step-by-step checklists for conducting quarterly employee access reviews, verifying cloud configuration drift, executing automated dependency vulnerability sweeps, testing backup restoration integrity, and reviewing firewall rule sets. We also configure automated alerting inside your communication channels (such as Slack or Microsoft Teams) to notify your engineering team immediately if an unapproved public bucket, wildcard IAM policy, or critical CVE is detected in production.
How long does it take to start?
Discovery starts within days of agreement. Builds run in weekly sprints with a demo every week.
Who owns the work?
You do, under a signed agreement — code, docs and accounts are handed over at the end.
Content last reviewed September 2026.
Straight Talk
Mistakes We Prevent & How We Compare
Common mistakes we prevent
Shared logins nobody owns — split into named accounts
Ex-staff accounts left active — revoked with evidence
Dependencies years out of date — inventoried and planned
Us vs the usual alternative
Output
AnyPlace: Ranked fixes with effort
Typical alternative: Scanner PDF nobody acts on
Tone
AnyPlace: Prioritized and practical
Typical alternative: Fear-driven upsell
Follow-up
AnyPlace: Re-check list included
Typical alternative: One-off report, no loop
Before
The starting point we usually find
Nobody knows who can access what; client security questionnaires go unanswered.
After
Where this service leaves you
Current access list, ranked fix plan with quick wins done, and evidence to answer any questionnaire.
Worth knowing: IBM's annual Cost of a Data Breach Report tracks average breach costs in the millions — most incidents trace back to basic access hygiene. Source: IBM Security · Verified September 2026
Related Services
Pairs Well With
Cloud Setup & DevOps
Cloud hosting setup, CI/CD pipelines and cost hygiene on AWS, Azure or GCP — with runbooks your team can follow.
View service→
Custom Software Development
Web platforms, business tools and APIs — planned in milestones, built in weekly sprints, handed over with docs and tests.
View service→
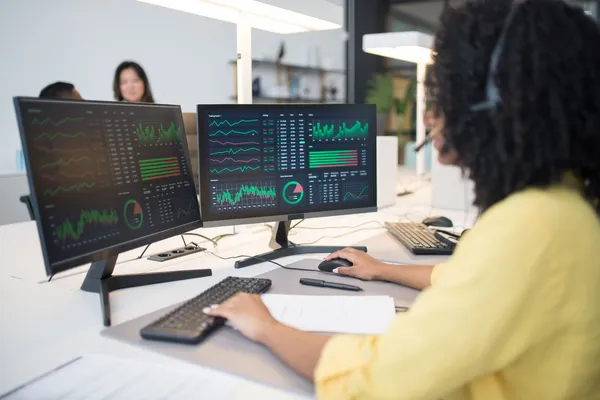
Data Pipelines & Dashboards
Centralize messy data from multiple tools into dashboards your leadership actually checks weekly.
View service→
TELL US ABOUT YOUR PROJECT
Tell Us What to Build, Fix or Modernize
Send a short brief. We reply within 12 hours with clarifying questions and a discovery quote — no retainers, no spam.
What Happens Next
Request a Discovery Quote
Share your goals and timeline. NDA signed first if needed.
12-hour response