Strategic IT Consulting: Engineered for Architectural Longevity
Objective advice before expensive commitments: we review your current systems, evaluate vendor options, and produce a clear, phased technical roadmap your leadership can trust.
Best for growing businesses in India, the USA, UK, Australia and Canada where you're planning a major software build, rewrite, or vendor switch and want an independent, technical opinion before writing checks. Fixed-price advisory engagement based on system scope; phased implementation oversight optional.
Executive Brief
Strategic Context & Engineering Purpose
How our IT consulting engagements de-risk operational transitions and produce enduring software assets.
Operational Challenge
Mid-market enterprises, scaling technology organizations, and private equity portfolio companies frequently find themselves trapped under the weight of compounding technical debt, un-documented legacy software systems, and skyrocketing cloud hosting bills. Executive leadership teams are regularly forced to make multi-million-dollar technology investments—such as core ERP migrations, custom software rebuilds, or cloud re-platforming—without objective, in-house technical validation. Relying on commission-driven vendor sales pitches or high-cost management consulting conglomerates (who assign junior analysts and deliver 200-page generic theoretical slide decks) results in catastrophic budget overruns, failed software implementations, and severe operational disruption.
Architectural Approach
We provide pragmatic, vendor-neutral IT consulting and software architecture advisory delivered exclusively by seasoned principal systems architects and former engineering CTOs. We do not accept referral commissions, reseller kickbacks, or vendor partnerships, ensuring our strategic recommendations serve your commercial and operational interests with 100% objectivity. Our consulting engagements begin with deep code-level and infrastructure-level audits, evaluating system scalability, security vulnerability posture, technical debt burdens, and cloud unit economics. We synthesize technical findings into executive-level Architecture Decision Records (ADRs), risk-ranked modernization roadmaps with realistic budget estimates, and phased migration blueprints that de-risk operational transitions.
Measured Economic Impact
Strategic architectural advisory eliminates thirty to fifty percent of unnecessary software and cloud expenditures by terminating redundant SaaS tools, rightsizing over-provisioned infrastructure, and preventing ill-advised vendor platform lock-in. Technical modernization roadmaps accelerate engineering release velocity by over forty percent while de-risking high-stakes database migrations and legacy cutovers through proven patterns like the Strangler Fig architecture. In M&A and private equity contexts, our formal technical due diligence audits uncover hidden liabilities, security vulnerabilities, and code quality risks before deal closure, protecting investment valuation and informing post-merger integration strategies.
Governance & IP Custody
We enforce radical transparency, strict objectivity, and unconditional intellectual property transfer throughout every advisory engagement. All audit reports, system topology blueprints, data flow diagrams, technology selection scoring matrices, and implementation runbooks are authored directly in your corporate documentation platforms (Confluence, Notion, or Git Markdown). We work alongside your executive leadership and internal engineering teams through transparent, collaborative discovery sessions. Upon project completion, all strategic artifacts, audit raw data, and executive presentation decks are transferred with complete corporate ownership.
Engineering Architecture
Core Technical Blueprints & Subsystems
Every system is modularized into isolated subsystems with strict interface contracts and automated testing.
Comprehensive Codebase, Architecture & Technical Debt Audits
Static code analysis, modular coupling evaluation, and SQALE debt scoring
Understanding the true operational health of a software system requires inspecting source code reality rather than reviewing outdated architectural diagrams. We execute exhaustive codebase and architecture audits across monolithic and microservice systems. We analyze code maintainability, test coverage gaps, circular dependencies, database schema normalization, and security vulnerability density using automated static analysis paired with manual senior architectural inspection. We calculate objective technical debt metrics using the SQALE methodology, identifying the exact high-friction modules that consume disproportionate maintenance effort and providing refactoring blueprints to restore engineering velocity.
Code & Schema Deliverables:
- Exhaustive technical audit report evaluating codebase health, architecture, and database schemas
- Quantitative technical debt assessment utilizing SQALE scoring and code churn hotspot analysis
- Risk-ranked remediation catalog detailing critical security, scalability, and maintainability bottlenecks
- Executive summary briefing translating technical liabilities into commercial risk and financial impact
Failure Modes Prevented:
- ✕Making multi-million-dollar technology investments based on inaccurate or superficial vendor assumptions
- ✕Catastrophic production scalability collapses during critical commercial traffic and sales surges
- ✕Sudden departure of key legacy engineers leaving the organization with un-audited, un-documented systems
- ✕Accumulation of hidden security vulnerabilities that expose customer data to regulatory penalties
Tech Stack
Cloud Infrastructure, FinOps & Security Posture Assessment
Well-Architected reviews, multi-cloud cost rightsizing, and CIS benchmark hardening
Organic cloud growth over years routinely leads to sprawling, disorganized cloud tenancies with uncontrolled monthly hosting expenditures. Our cloud architects conduct comprehensive Well-Architected Framework reviews across AWS, GCP, and Azure environments. We evaluate network segmentation, disaster recovery preparedness, database high-availability configurations, and IAM identity boundaries against CIS Benchmarks. On the financial governance side, our FinOps audit identifies unattached storage volumes, over-provisioned compute instances, and inefficient data transfer routes, delivering an actionable rightsizing roadmap that permanently cuts monthly cloud bills by thirty to fifty percent.
Code & Schema Deliverables:
- Cloud Security and Well-Architected Framework review report across AWS, Azure, or GCP
- Comprehensive FinOps cost reduction blueprint detailing exact compute and storage rightsizing actions
- Disaster recovery and business continuity audit evaluating verified RTO and RPO benchmarks
- Network architecture topology diagrams detailing VPC peering, subnets, and zero-trust perimeters
Failure Modes Prevented:
- ✕Shocking end-of-month cloud bills caused by untracked compute provisioning and orphaned cloud storage
- ✕Catastrophic data loss resulting from reliance on theoretical, un-tested backup and disaster recovery plans
- ✕Regulatory compliance audit failures (SOC 2, HIPAA, ISO 27001) due to misconfigured cloud security groups
- ✕Extended production outages caused by single points of failure in single-availability-zone architectures
Tech Stack
Vendor-Neutral Technology Selection & PoC Feasibility Prototyping
Weighted multi-criteria evaluation matrices and rapid architectural prototyping
Selecting the wrong foundational technology stack, ERP platform, or database engine can cost millions and paralyze engineering agility for years. We provide rigorous, vendor-neutral technology evaluation frameworks tailored to your unique commercial workflows and internal engineering capabilities. We construct weighted evaluation matrices scoring candidate platforms across total cost of ownership, developer ecosystem maturity, API extensibility, vendor viability, and data portability. To eliminate theoretical speculation, our principal architects build rapid Proof-of-Concept (PoC) prototypes that stress-test critical operational integrations and performance bottlenecks under real-world conditions before corporate commitments are made.
Code & Schema Deliverables:
- Vendor-neutral technology evaluation matrix scoring candidate platforms against weighted business criteria
- Comprehensive Total Cost of Ownership (TCO) financial model covering 3-year licensing, hosting, and dev costs
- Functional Proof-of-Concept (PoC) prototype codebase validating critical integration and performance risks
- Final architectural recommendation report with executive decision consensus documentation
Failure Modes Prevented:
- ✕Vendor lock-in trap where proprietary platforms extract compounding annual licensing rate increases
- ✕Selecting over-hyped, immature open-source frameworks that lack commercial ecosystem support
- ✕Costly multi-year enterprise software implementations that are abandoned due to poor workflow fit
- ✕Biased vendor selection driven by software sales commissions and aggressive partner incentives
Tech Stack
Legacy Modernization & Strangler Fig Migration Blueprints
Incremental modernization roadmaps with zero downtime and verified rollback gates
Attempting high-risk 'big-bang' software rewrites almost always ends in catastrophic project failure, blown budgets, and missed deadlines. We engineer pragmatic, low-risk legacy modernization roadmaps utilizing the proven Strangler Fig architectural pattern. We design an intermediary API facade and event bridge that intercepts customer traffic, routing newly modernized features to scalable microservices or modular modern components while allowing the core legacy system to continue operating stably in parallel. System by system, database by database, legacy dependencies are systematically retired in controlled sprint milestones with zero downtime and verified rollback gates.
Code & Schema Deliverables:
- Phased legacy modernization roadmap specifying exact subsystem decoupling sequences and milestones
- Intermediary API facade and routing architecture blueprint enabling side-by-side legacy and modern execution
- Data migration and event synchronization plan ensuring transactional consistency during transition
- Risk mitigation matrix and rollback runbooks for every phased architectural transition milestone
Failure Modes Prevented:
- ✕Multi-million-dollar 'big bang' rewrite disasters that fail to deploy after years of expensive development
- ✕Business operations paralyzed by downtime or broken workflows during major system cutovers
- ✕Data corruption and financial ledger drift between legacy databases and modern application layers
- ✕Executive and investor loss of confidence caused by delayed, un-phased monolithic software projects
Tech Stack
Engineering Governance
Engineering Standards, QA & Security Protocols
Rigorous development disciplines that protect your code quality, deployment velocity, and infrastructure security.
Architecture Decision Records (ADRs) & C4 Model Diagrams
Architectural GovernanceAll architectural recommendations are documented using standardized Architecture Decision Records (ADRs) specifying operational context, alternatives evaluated, and trade-offs. System architectures are visualized using the C4 Model (Context, Containers, Components, Code).
Tooling & Rails
Quantitative Technical Debt Scoring (SQALE Method)
Code Quality EvaluationCodebase audits evaluate technical debt using the Software Quality Assessment based on Lifecycle Expectations (SQALE) methodology. Codebases are scored objectively on maintainability, testability, security, and reliability, identifying exact refactoring hours required.
Tooling & Rails
Vendor-Neutral Evaluation Scoring with Weighted Criteria
Strategic ObjectivityVendor and platform evaluations utilize structured scoring matrices with weighted commercial and technical criteria agreed with leadership upfront. Evaluators have zero financial ties, affiliate agreements, or reseller relationships with evaluated vendors.
Tooling & Rails
Strangler Fig Migration Pattern with Zero-Downtime Rollback
Migration DisciplineLegacy system modernization blueprints enforce the Strangler Fig pattern. New services are deployed behind an API routing facade, intercepting fractional traffic in phases with automated health checks and immediate rollback capabilities.
Tooling & Rails
Production Case Evidence
Detailed Architecture Problem-Solution Blueprints
Real-world engineering case blueprints detailing baseline bottlenecks, technical intervention, and verified production metrics.
Operational Bottleneck & Root Cause
The firm was considering a $2.5M complete rewrite of their 12-year-old core dispatch platform after the legacy development team claimed it could no longer be maintained.
Root Cause: Technical debt had accumulated in three specific monolithic controllers, but 80% of the underlying business logic and database schema was robust and scalable.
Engineered Architecture
Conducted an intensive two-week code and architecture audit; designed a targeted refactoring roadmap replacing only the three bottleneck controllers using modern microservices.
Measured Result
Saved $1.8M by avoiding an unnecessary full rewrite; restored engineering feature velocity in 90 days; platform passed SOC 2 Type II audit flawlessly.
Operational Bottleneck & Root Cause
The retailer was pitched a $1.4M enterprise ERP suite by a commission-driven sales agency, which would have required rewriting their entire point-of-sale workflow.
Root Cause: Lack of in-house technical architecture expertise to evaluate whether the proposed ERP was appropriate for their lean, distributed store operations.
Engineered Architecture
Performed a vendor-neutral technology evaluation and built a functional Proof-of-Concept demonstrating that a modern headless commerce platform with API bridges met 100% of needs.
Measured Result
Reduced capital investment from $1.4M to $320K; deployed in four months instead of eighteen; avoided long-term proprietary ERP vendor lock-in.
Operational Bottleneck & Root Cause
Cloud hosting bills on AWS had grown to $65,000 monthly with frequent database connection timeouts during market open hours, threatening user retention.
Root Cause: Over-provisioned EC2 instances running un-cached database queries, thousands of unattached EBS volumes, and lack of read-replica database routing.
Engineered Architecture
Executed an infrastructure FinOps and database architecture audit; added Redis caching layers, implemented Aurora read replicas, and right-sized compute.
Measured Result
Monthly cloud hosting bill dropped from $65,000 to $28,000 (57% recurring savings); eliminated 100% of database timeout errors during market open surges.
Operational Bottleneck & Root Cause
Loan application processing was stalled because the legacy on-premise loan origination system could not integrate with modern consumer mobile banking apps.
Root Cause: Proprietary database with closed binary formats and lack of RESTful or event-driven API endpoints for third-party system integration.
Engineered Architecture
Architected a secure API gateway facade with Change Data Capture (CDC) streaming loan updates to an isolated, encrypted cloud database with mobile endpoints.
Measured Result
Enabled mobile loan applications in 60 days; loan application volume grew by 85%; core legacy mainframe remained untouched and stable.
Sprint Delivery Cadence
Phased Sprint Roadmap & Quality Gates
Predictable milestone delivery with working software demoed every week in your repository.
Phase 01: System Discovery, Stakeholder Interviews & Access Provisioning
Operational discovery, code repository access, architecture documentation, and cloud audits
Deliverables:
- Executive and engineering stakeholder discovery interviews mapping operational friction points
- Comprehensive codebase, repository, and cloud infrastructure access setup under NDA
- Initial system topology and data flow diagram mapping current-state architecture
- Automated static analysis tooling deployment (SonarQube/Semgrep) across target codebases
Gate Criteria
Completed stakeholder discovery and successful automated scan execution across all code repositories.
Phase 02: Deep Technical Audit, FinOps & Security Posture Review
Code analysis, database schema review, cloud cost audit, and technical debt scoring
Deliverables:
- Codebase quality and maintainability evaluation report detailing SQALE technical debt scores
- Database performance and schema normalization audit identifying query bottlenecks and scaling limits
- Cloud infrastructure FinOps review identifying immediate rightsizing and cost elimination actions
- Security posture and vulnerability assessment evaluating cloud assets against CIS Benchmarks
Gate Criteria
Delivery of preliminary audit findings and alignment review with technical leadership.
Phase 03: Technology Evaluation, Vendor Matrix & PoC Prototyping
Vendor evaluation scoring, TCO financial modeling, and rapid PoC prototyping
Deliverables:
- Weighted vendor-neutral technology evaluation matrix scoring candidate platform options
- Three-year Total Cost of Ownership (TCO) financial model covering licensing, hosting, and dev
- Functional Proof-of-Concept (PoC) prototype codebase validating critical integration risks
- Formal Architecture Decision Records (ADRs) documenting recommended technical foundations
Gate Criteria
Validated PoC prototype execution proving feasibility of recommended architectural approach.
Phase 04: Modernization Roadmap, Executive Briefing & Handover
Phased migration blueprint, budget/timeline estimates, executive presentation, and handover
Deliverables:
- Phased legacy modernization roadmap specifying sprint milestones, dependencies, and gates
- Executive decision deck presenting strategic findings, ROI analysis, and risk mitigation
- Detailed engineering RFP and implementation specifications for procurement or internal teams
- Complete transfer of all audit models, documentation, code prototypes, and strategic artifacts
Gate Criteria
Executive leadership sign-off on modernization roadmap and complete delivery of all audit assets.
Financial Transparency
Total Cost of Ownership & Risk Mitigation
Understand the core technical variables that dictate development investment and long-term operating costs.
Objective Architectural Guidance vs Failed Multi-Million-Dollar Rewrites
TCO VariablePrimary Cost Driver
Industry research by Standish Group demonstrates that over 70% of enterprise software rewrites fail, exceed budget, or deliver zero business value.
Risk Without Proper Architecture
Organizations gamble millions on high-risk 'big bang' rewrites that end in catastrophic project abandonment and leadership turnover.
Our Engineering Mitigation
Our independent audits identify targeted refactoring and Strangler Fig modernization blueprints, achieving goals at a fraction of rewrite costs.
Vendor-Neutral Advisory vs Biased Software Reseller Markups
TCO VariablePrimary Cost Driver
Software sales agencies and certified implementation partners earn 20-40% recurring commissions by selling specific proprietary enterprise platforms.
Risk Without Proper Architecture
Companies are steered into bloated, overpriced enterprise software contracts that enrich the reseller while failing operational needs.
Our Engineering Mitigation
We maintain 100% vendor neutrality with zero commission partnerships, ensuring our evaluations strictly optimize your bottom-line ROI.
Proactive FinOps Rightsizing vs Compounding Cloud Waste
TCO VariablePrimary Cost Driver
Sprawling cloud tenancies accumulate 30-50% financial waste through over-provisioned instances, unattached disks, and untracked dev resources.
Risk Without Proper Architecture
Organizations hemorrhage tens of thousands of dollars monthly in unnecessary cloud hosting bills that drain growth capital.
Our Engineering Mitigation
Our FinOps audit identifies exact rightsizing actions and commitment strategies, typically saving more in cloud costs than the audit fee itself.
Technical Due Diligence vs Unforeseen Post-Acquisition Liabilities
TCO VariablePrimary Cost Driver
Acquiring or investing in a software company without rigorous technical due diligence exposes investors to hidden code debt and security breaches.
Risk Without Proper Architecture
Investors discover post-close that acquired software requires a complete rebuild, destroying investment returns and growth models.
Our Engineering Mitigation
Our 10-day M&A technical due diligence audits uncover hidden architecture flaws and compliance risks, protecting investment valuations.
Results
What This Service Delivers
Outcome 1
A clear audit of technical debt, risks and bottlenecks
An objective, code-level audit of technical debt, security posture, and cloud cost efficiency.
Outcome 2
A vendor-neutral evaluation of platforms and tools
A vendor-neutral evaluation of technology options with 3-year TCO financial modeling — zero sales commission bias.
Outcome 3
A phased roadmap your board and engineers both trust
A phased, risk-ranked modernization roadmap with realistic timelines, resource requirements, and rollback gates.
Fit Check
Is This Service Right for Your Business?
When It Fits
You're planning a major software build, rewrite, or vendor switch and want an independent, technical opinion before writing checks.
✕When It Doesn't
You need a full-time interim CTO for 12 months — we provide focused advisory and roadmaps, not executive seat coverage.
Use Cases
Business Use Cases We Serve
Planning a major rebuild
Team says rewrite everything, management fears the bill — an independent audit determining what to keep, fix, or replace.
Cloud costs spiraling
Hosting bills grow monthly with no clear owner — architecture and FinOps audit rightsizing spend by 30-50%.
M&A technical diligence
Evaluating a software acquisition or investment — deep code, architecture and security due diligence within 10 days.
Gallery
What Typical Deliverables Look Like
Sample deliverables from a typical engagement — yours follow the same shape, scoped to your business.
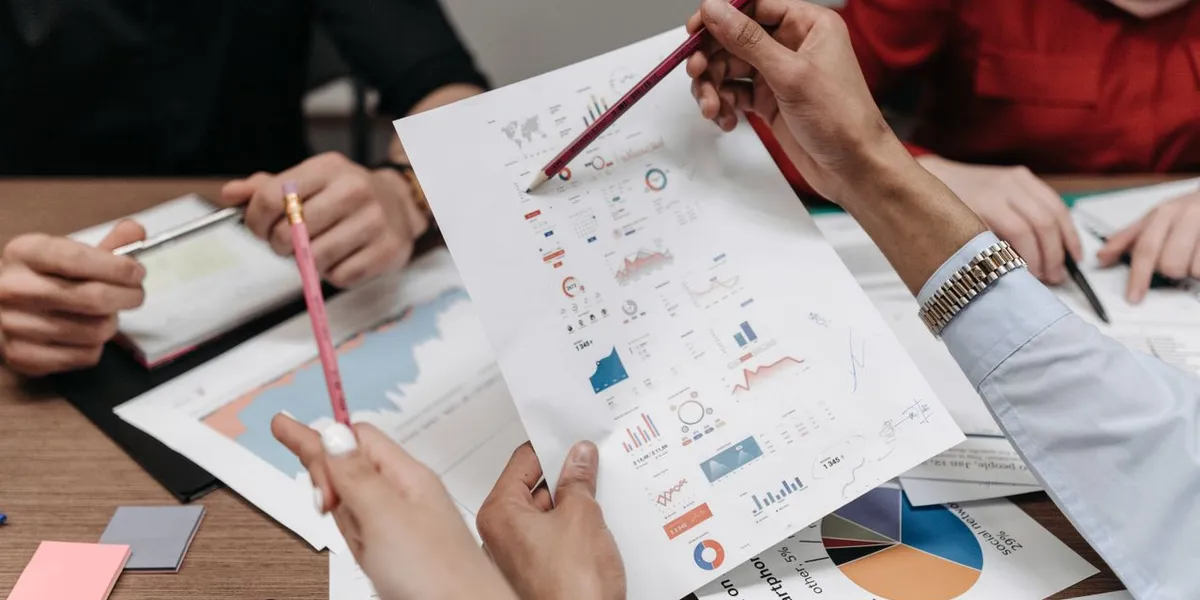
Visual 1
Technical audit report
Code health, security vulnerabilities and technical debt scored objectively.
Visual 2
Vendor evaluation matrix
100% vendor-neutral scoring across TCO, fit and scalability with zero commissions.
Visual 3
Phased modernization roadmap
Strangler Fig migration blueprints de-risking system cutovers with zero downtime.
Timeline
How Long Does IT consulting Take?
Advisory review typically 1–3 weeks, depending on system complexity. The same four delivery stages run every engagement — you approve progress at each gate before the next begins.
Stage 1
System discovery
Deep dive into your codebase, cloud accounts, architecture docs and operational pain points with key stakeholders.
Stage 2
Technical audit
Rigorous inspection of code health, technical debt, database schemas, cloud infrastructure and security controls.
Stage 3
Options & modeling
Vendor-neutral evaluation of architectural paths, TCO financial modeling and rapid PoC feasibility prototyping.
Stage 4
Roadmap & briefing
Phased modernization roadmap with clear milestones, executive presentation and complete documentation handover.
Pricing
What Drives the Cost of IT consulting?
- 1
Number of applications, repositories and cloud tenancies
- 2
Depth of code inspection, security testing and PoC prototyping
- 3
Urgency and timeline (e.g. 10-day M&A diligence versus 4-week audit)
Pricing shape: Fixed-price advisory engagement based on system scope; phased implementation oversight optional.
Indicative ranges live on the pricing page — your fixed quote arrives with the discovery scope.
Process
Delivery Stack and Pricing
Stages shown above — here is what they run on and how they are priced.
Stack & Tools
Enterprise Architecture (TOGAF)AWS / Azure Cloud EconomicsTerraformKubernetesSonarQube Code AuditsSOC 2 & ISO 27001 CompliancePostgreSQL / MicroservicesJira / ConfluenceLucidchart / MiroDatadog / DynatraceGitHub / CI/CDDocker
Pricing Shape
Fixed-price advisory engagement based on system scope; phased implementation oversight optional.
Due Diligence
Technical Due Diligence FAQs
How much does IT consulting cost?
After a short paid discovery (typically 1–3 weeks) you receive a fixed price with milestones. Fixed-price advisory engagement based on system scope; phased implementation oversight optional. Discovery is credited toward the build if you proceed.
How does your IT consulting differ from traditional large management consulting firms?
Traditional management consulting conglomerates (like the Big Four or legacy IT consultancies) typically assign junior generalist MBAs who rely on pre-packaged slide templates, conduct surface-level executive interviews, and produce theoretical 200-page reports without ever inspecting a single line of code or cloud console configuration. Furthermore, many legacy firms have lucrative reseller partnerships with enterprise software vendors, creating inherent conflicts of interest. Our IT consulting is led exclusively by seasoned principal software architects and former engineering CTOs who roll up their sleeves, inspect Git repositories, run database query analyzers, audit cloud infrastructure, and build functional code prototypes. We do not accept vendor commissions, guaranteeing 100% objective, actionable guidance that engineering teams respect and executive boards trust.
What is the Strangler Fig modernization pattern, and why is it superior to a complete system rewrite?
The Strangler Fig pattern—named after vines that grow around a host tree until they replace it—is an architectural strategy for incrementally modernizing legacy software without the massive risk of a 'big bang' rewrite. In a rewrite, development teams spend one to two years building a new system from scratch while the legacy system continues evolving, almost always resulting in blown budgets, feature parity drift, and catastrophic launch day outages. With the Strangler Fig pattern, we deploy an API routing facade in front of the legacy system. We then extract one specific high-friction workflow (such as customer billing or inventory lookup) into a modern microservice or modular component, routing traffic to the new service while leaving the rest of the legacy system running stably. Over time, the new architecture systematically replaces legacy components in safe, verified phases with zero business downtime.
How do you evaluate whether our legacy software should be refactored, re-platformed, or completely replaced?
We evaluate legacy systems using a structured, quantitative decision framework across four primary dimensions: Business Value, Technical Maintainability, Security/Compliance Risk, and Total Cost of Ownership (TCO). First, we profile the codebase to identify 'hotspots'—areas of high code churn and high defect frequency. Often, eighty percent of an organization's bugs and friction reside in just ten to fifteen percent of the codebase, which can be refactored or decoupled without touching stable core routines. We evaluate whether the core relational database schema is sound; if the underlying data model is robust, preserving the database while modernizing the API and frontend presentation layer is vastly cheaper and faster than a full replacement. If a system is fundamentally unmaintainable, lacks security support, or uses obsolete programming languages, we recommend a phased replacement blueprint.
What does an M&A or private equity technical due diligence audit cover?
Our private equity and M&A technical due diligence audits provide investors and acquirers with an unvarnished assessment of target software assets within a rapid 10-to-14 day window. We evaluate five core pillars: Architecture & Scalability (ability of systems to support 3x-5x transaction growth), Code Quality & Technical Debt (maintainability, test coverage, modularity using SQALE scoring), Cybersecurity & Compliance (SOC 2, HIPAA, GDPR readiness, vulnerability scans, credential hygiene), Open Source License Governance (SBOM scanning to detect copyleft GPL contamination), and Engineering Team & Process Health (deployment velocity, bus factor, key-person dependencies). We deliver an executive red-flag report and post-close 100-day engineering value creation roadmap.
How do you help companies cut their monthly AWS, Azure, or Google Cloud bills?
Our FinOps cloud optimization advisory begins with an exhaustive cloud consumption audit. We analyze 30-to-90 day resource utilization percentiles across all cloud accounts. We immediately identify and remediate low-hanging waste: terminating unattached EBS storage volumes, unassociated Elastic IP addresses, outdated development environments running 24/7, and orphaned snapshot backups. Next, we right-size over-provisioned virtual machines and database instances, transition underutilized workloads to modern ARM-based compute (like AWS Graviton), implement container auto-scaling with spot instances via Karpenter, and configure automated S3 intelligent tiering. Finally, we advise leadership on structured Savings Plans and Reserved Instance commitments, typically slashing monthly cloud infrastructure expenses by 30% to 50% permanently.
What is an Architecture Decision Record (ADR), and why is it valuable for our engineering team?
An Architecture Decision Record (ADR) is a lightweight, structured document that captures an important architectural choice made by engineering leadership, along with the operational context, alternatives considered, and long-term consequences. ADRs are authored in Markdown and committed directly inside your Git repository alongside source code. ADRs provide immense organizational value: they prevent future engineering teams from inadvertently repeating past failed experiments, eliminate circular debates during code reviews, preserve institutional memory when senior engineers depart, and dramatically accelerate the onboarding of new engineering hires by clearly explaining the 'why' behind system architecture.
Can you help our company prepare for a formal SOC 2 Type II, ISO 27001, or HIPAA compliance audit?
Yes. We bridge the critical gap between abstract compliance requirements and concrete engineering implementation. We evaluate your current technical posture against the target compliance framework, identify configuration and policy gaps, and provide exact remediation blueprints. We assist with configuring multi-account cloud landing zones with strict VPC isolation, enforcing multi-factor authentication (MFA) with SSO, implementing customer-managed KMS envelope encryption, establishing immutable CloudTrail audit logging, and setting up automated dependency vulnerability scanning in your CI/CD pipelines. We work directly alongside your compliance automation platform (such as Vanta, Drata, or Secureframe) to ensure all automated technical evidence checks pass.
How long does a strategic IT consulting or architecture audit engagement typically take?
Our strategic advisory engagements are focused, agile, and time-boxed to deliver immediate executive clarity. A rapid technical due diligence audit or targeted cloud FinOps review is typically completed in 1 to 2 weeks. A comprehensive enterprise architecture and codebase audit—including static code analysis, stakeholder interviews, database performance reviews, and phased modernization roadmapping—typically spans 3 to 4 weeks. Every engagement operates on a transparent fixed-price scope with weekly milestone readouts, ensuring you receive immediate actionable findings rather than waiting weeks for a final presentation.
Who owns the audit reports, architecture blueprints, and proof-of-concept code upon completion?
Your organization maintains one hundred percent exclusive, unconditional ownership of all audit documentation, system topology diagrams, data flow models, vendor evaluation matrices, Architecture Decision Records, and custom Proof-of-Concept prototype code. Everything is delivered directly into your corporate repositories, Confluence/Notion workspaces, and cloud tenancies. We do not retain proprietary licensing claims or restrict how you utilize, distribute, or implement the strategic recommendations.
Can your team oversee or implement the modernization roadmap after the advisory engagement concludes?
Yes. While our consulting engagements are self-contained and deliver complete operational autonomy for your internal team or third-party vendors, many clients choose to partner with us for implementation. We offer flexible ongoing options: providing senior architectural oversight (acting as an advisory board to review pull requests and ensure roadmap adherence), embedding dedicated engineering pods to execute complex core refactoring milestones, or providing end-to-end turnkey delivery of the modernized platform with weekly staging demonstrations.
How long does it take to start?
Discovery starts within days of agreement. Builds run in weekly sprints with a demo every week.
Who owns the work?
You do, under a signed agreement — code, docs and accounts are handed over at the end.
Content last reviewed September 2026.
Straight Talk
Mistakes We Prevent & How We Compare
Common mistakes we prevent
Trusting software vendors or commission-driven resellers for architecture advice
Attempting high-risk 'big bang' rewrites instead of phased Strangler Fig modernizations
Making technology decisions without inspecting actual codebase reality and data models
Us vs the usual alternative
Objectivity
AnyPlace: 100% vendor-neutral, zero commissions
Typical alternative: Sales partners pushing software licenses
Depth
AnyPlace: Code-level and infrastructure-level audit
Typical alternative: High-level slide decks with no code inspection
Output
AnyPlace: Actionable phased roadmap with PoCs
Typical alternative: Theoretical 200-page report nobody reads
Before
The starting point we usually find
Leadership paralyzed by technical debt debates and vendor sales pitches; fear of making a costly software mistake.
After
Where this service leaves you
Clear, evidence-based architectural roadmap with objective numbers — leadership and engineering aligned on the path forward.
Worth knowing: The Standish Group's Chaos Report reveals that over 70% of enterprise software rewrites fail, exceed budget, or deliver zero business value — independent architectural advisory prevents costly mistakes. Source: The Standish Group · Verified September 2026
Related Services
Pairs Well With
Custom Software Development
Web platforms, business tools and APIs — planned in milestones, built in weekly sprints, handed over with docs and tests.
View service→
Cloud Setup & DevOps
Cloud hosting setup, CI/CD pipelines and cost hygiene on AWS, Azure or GCP — with runbooks your team can follow.
View service→
Security Reviews & Hardening
Config and code reviews, access cleanup and fix lists prioritized by risk — no scare tactics, just actionable reports.
View service→
TELL US ABOUT YOUR PROJECT
Tell Us What to Build, Fix or Modernize
Send a short brief. We reply within 12 hours with clarifying questions and a discovery quote — no retainers, no spam.
What Happens Next
Request a Discovery Quote
Share your goals and timeline. NDA signed first if needed.
12-hour response